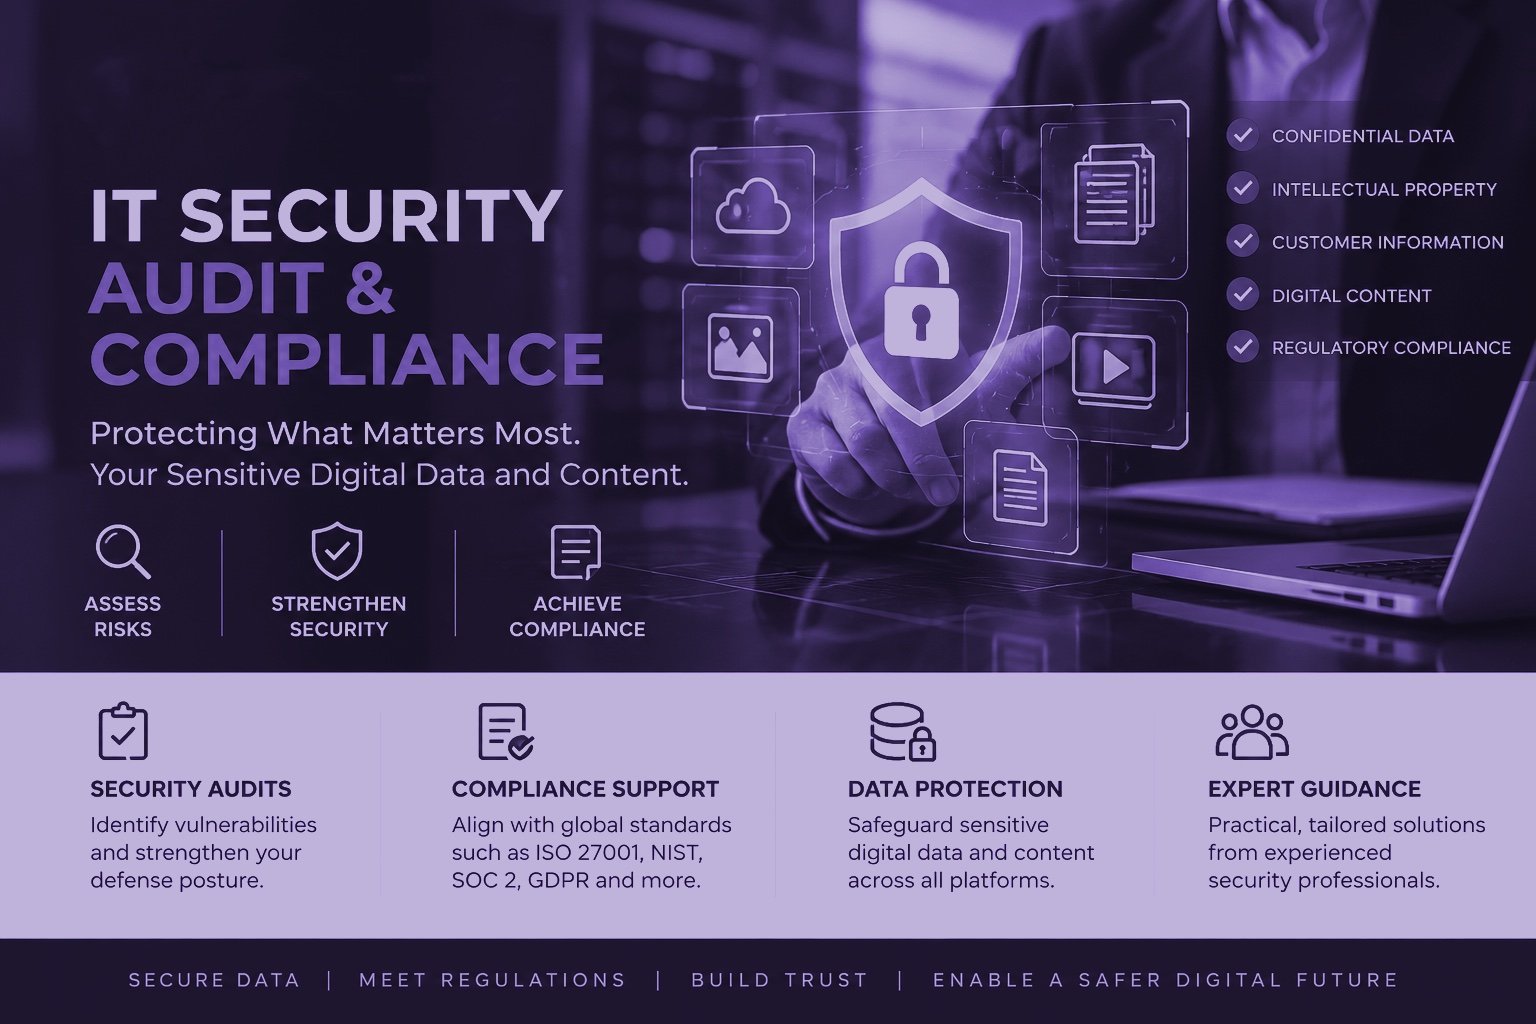
IT SECURITY AUDIT AND COMPLIANCE SERVICES IN LOS ANGELES
LEADER IN IT SECURITY AUDIT & COMPLIANCE.
We help studios achieve TPN security compliance by ensuring your IT infrastructure meets the strict security requirements of leading content providers such as Netflix, Disney, HBO, Warner Bros., Fox, Paramount, Amazon, and Apple.
IT SECURITY AUDIT
PREP AND CONSULTING
My Remote Tech helps organizations get ready for internal and external security audits by finding gaps, fixing weaknesses, and organizing the evidence auditors need. The goal is to pass audits with confidence, reduce risk, and meet compliance requirements required by MPA security requirements maintained by TPN for media and entertainment and technology industry.
What is IT security audit preparation?
IT security audit preparation is the process of reviewing your systems, policies, and controls before an official audit. Consultants run a readiness assessment, compare your current security posture against the required framework, and give you a clear plan to close any gaps before the auditor arrives.
What does an IT security consultant do during audit prep?
An IT security consultant assesses your network, access controls, data protection, and incident response processes. They identify vulnerabilities, help write or update security policies, map controls to compliance standards, and prepare the documentation and evidence auditors will request.
Why is audit preparation important?
Preparing ahead of an audit reduces the risk of failed findings, costly remediation, and certification delays. It also strengthens your overall cybersecurity, builds trust with customers and partners, and shows regulators that your organization takes data protection seriously. For media and entertainment vendors, readiness is especially critical: major studios and streaming platforms such as Disney, Netflix, Paramount, Amazon, and Apple often require a Trusted Partner Network (TPN) security assessment before sharing pre-release content.
Who needs IT security audit consulting?
Any business that handles sensitive content and wants to work with major studios and streaming platforms such as Amazon, Apple, Netflix, Disney, Warner Bros., and Paramount can benefit from audit preparation. These companies typically expect vendors to follow MPA content security best practices and complete a Trusted Partner Network (TPN) assessment, making TPN readiness an essential first step for new vendors.
🧭 1. Objectives of an IT Security Audit
Identify vulnerabilities across network, systems, and data storage.
Evaluate effectiveness of existing security controls.
Ensure compliance with regulations (e.g., HIPAA, GDPR, PCI-DSS, SOC 2).
Mitigate risk of breaches, data loss, or unauthorized access.
Prepare for formal certification or government audits.
🛠 2. Core Components of the Audit
Network Security: Firewalls, IDS/IPS, segmentation, remote access controls
System Security: OS patching, endpoint protection, admin access
Data Protection: Encryption (in transit/at rest), DLP, backups
Identity & Access Management (IAM): MFA, SSO, least privilege enforcement
Policy & Documentation: Security policies, incident response plans, change logs
Physical Security: Access to data centers, surveillance, device disposal
Application Security: Secure coding practices, vulnerability testing
Third-Party Risk:Vendor security reviews and contract compliance
📜 3. Compliance Standards (Examples)
TPN: Industry-wide campaign that helps organizations improve content security through practical resources, education and action, regardless of their size, budget, or security maturity.
HIPAA: HealthcarePatient data privacy and security
PCI-DSS: Payment processingSecure handling of credit card data
SOC 2: SaaS, cloud service providersSecurity, availability, confidentiality
ISO 27001: Any industryInformation security management systems
🔍 4. Audit Process Flow
Pre-Audit Preparation
Define scope and objectives
Identify assets and stakeholders
Risk Assessment
Evaluate threats, vulnerabilities, and likelihood
Security Control Evaluation
Test technical and administrative controls
Documentation Review
Policies, logs, reports, and user access records
Gap Analysis
Compare current posture vs. standard/compliance
Reporting
Audit findings, risk rating, remediation roadmap
Remediation & Follow-up
Patch gaps, revise policies, re-test if needed
📈 5. More Practices
Regular internal and third-party audits
Continuous monitoring (SIEM, vulnerability scanning)
Clear documentation and version control
Security awareness training
Network Vulnerability Management
Penetration Testing
What is an IT Security Audit and what are the focus points?
An IT security audit involves a thorough examination of an organization's information systems to evaluate its security posture. The audit focuses on the following aspects:
Assessment of Security Policies: Reviewing the organization’s existing security policies and ensuring they align with best practices.
Security Risk Assessment: identifies, assesses, and implements key security controls for organization network, physical security, and digital security.
Vulnerability Scanning: Identifying potential vulnerabilities within the system, network, or applications.
Penetration Testing: Actively attempting to exploit vulnerabilities to assess the effectiveness of security controls.
User Access Controls: Reviewing how user access to systems and data is managed, including authentication and authorization mechanisms.
Incident Response Plans: Checking if the organization has adequate plans for responding to security breaches.
Business Continuity, Backup Plan, Disaster Recovery Plan, Media Workflow and Network Topology Diagrams, and SIEM.
System and Network Monitoring: Ensuring effective monitoring is in place to detect suspicious activities.
- Audit Report: A detailed report highlighting findings, areas of non-compliance, and potential vulnerabilities.
- Risk Assessment: Identifying and categorizing risks based on their impact and likelihood.
- Remediation: Steps to remediate any identified security gaps.
IT Compliance:
Compliance refers to adhering to laws, regulations, standards, and guidelines that apply to the IT infrastructure and data management. Common compliance standards include:
- GDPR (General Data Protection Regulation): Protects the personal data of individuals within the EU.
- HIPAA (Health Insurance Portability and Accountability Act): Ensures the protection of sensitive patient data in the healthcare industry.
- PCI DSS (Payment Card Industry Data Security Standard): A set of requirements for securing payment card information.
- SOX (Sarbanes-Oxley Act): Affects financial record management and disclosure in publicly traded companies.
- ISO/IEC 27001: International standard for managing information security.
Compliance checks typically ensure:
- Data Protection: Appropriate measures are in place for the protection of sensitive data.
- Data Encryption: Ensuring that sensitive data is encrypted in storage and transit.
- User Consent: Ensuring users’ data is collected, stored, and processed with proper consent (GDPR).
- Documentation: Documenting processes and security controls for review by regulatory bodies.
The Relationship Between IT Security Audits and Compliance:
- Audit as a Compliance Requirement: Many regulatory frameworks require organizations to conduct regular security audits.
- Continuous Improvement: Audits often reveal areas where compliance might be lacking, helping organizations enhance their security posture.
- Risk Mitigation: Both compliance and security audits help mitigate risks of data breaches and financial penalties due to non-compliance.
We understand the key to success and safety for our clients organizations. Leave the security and compliance aspect to our experts, so that you can fully concentrate on unleashing your creativity. We work closely with you to fully understand your needs, ensuring that we can adhere to your specific compliance regulations and prevent leaks, breaches, and hacks from happening.
TPN IT Security Audit & Compliance Services Include:
Security Program Development
Policies and Controls Development
Network/Firewall/Workflow Diagram
Security Risk Assessment
IT Infrastructure Security Reviews
Penetration Testing
Vulnerability Monitoring & Testing
Security Awareness Training
TPN Assessment Prep & Remediation
TPN Onsite & Remote Assessments
TPN IT Security Audit & Compliance Consulting, Prep, and Remediation
The TPN IT Security Audit & Compliance Consulting & prep service provides end-to-end support for organizations seeking to align with the Trusted Partner Network (TPN) security standards — the global benchmark for protecting media content across production, post-production, and distribution workflows. Our service helps studios, vendors, and service providers achieve and maintain TPN certification through a combination of technical auditing, compliance consulting, and hands-on remediation.
1. Audit & Gap Assessment
Initial Assessment: Conduct a comprehensive review of your IT infrastructure, policies, and processes against TPN MPA (Motion Picture Association) security requirements.
Gap Analysis: Identify compliance gaps in areas such as:
Physical and logical access controls
Network and perimeter security
Endpoint protection and encryption
Content handling and data transfer security
Cloud environment configuration
Vendor and subcontractor management
Risk Prioritization: Classify vulnerabilities by severity and potential impact on TPN compliance.
2. Compliance Consulting
TPN Readiness Strategy: Develop a roadmap for meeting TPN audit requirements with practical, cost-effective steps.
Policy & Documentation Support: Draft or refine your:
Information Security Policy
Incident Response Plan
Access Control & Password Policy
Asset Management & Media Handling Procedures
Vendor Risk Management Policy
Guidance on Controls Implementation: Provide advisory on technical measures (firewalls, SIEM, DLP, VPN, MFA, etc.) to align with TPN standards.
Audit Preparation Coaching: Train internal teams to prepare for the TPN audit process and documentation requests.
3. Remediation & Execution
Implementation Assistance: Execute or assist in implementing corrective actions identified during the gap analysis phase.
Technical Hardening: Configure systems, network devices, and endpoints per TPN control objectives (e.g., secure remote access, content segregation, and data encryption).
Evidence Collection: Gather and format audit evidence (logs, screenshots, reports) per TPN audit submission standards.
Pre-Audit Validation: Conduct an internal “mock audit” to verify readiness before the official TPN auditor review.
4. Continuous Compliance & Maintenance
Ongoing Monitoring: Set up monitoring systems to maintain compliance posture (e.g., vulnerability scanning, log review, endpoint compliance).
Periodic Reassessment: Offer quarterly or semi-annual reviews to maintain alignment with evolving TPN and MPA guidelines.
Re-Certification Support: Help with the renewal or re-validation process for subsequent TPN assessments.
Deliverables
Comprehensive Security Assessment Report
Updated Comprehensive Security Policies & Procedures Documentation (ISMS = Information Security Management System) (structured framework of policies, procedures, and controls designed to systematically manage an organization's sensitive data and mitigate security risks.)
Technical Configuration Checklist
Security Risk Assessment
Network Vulnerability Scan Report
Penetration Testing
Audit Readiness Report for submission to TPN auditors
Remediation Roadmap with timelines and responsibilities
AI-Powered Cybersecurity & Compliance for Post-Production Agencies.
What Is an IT Security Audit and Compliance Assessment?
An IT security audit and compliance assessment is an independent review of an organization's cybersecurity tools, practices, and policies. It verifies that the organization meets the requirements of relevant laws, regulations, and industry standards, such as SOC 2, ISO 27001, and the Trusted Partner Network (TPN) assessment for media and entertainment.
The primary goal is to confirm that IT practices align with established frameworks, effectively protect sensitive data, and reduce risk. These audits are especially critical in industries where data privacy and confidentiality are top priorities, including healthcare, finance, technology, and media and entertainment.
Contact us here if you have any questions.